

Compliance
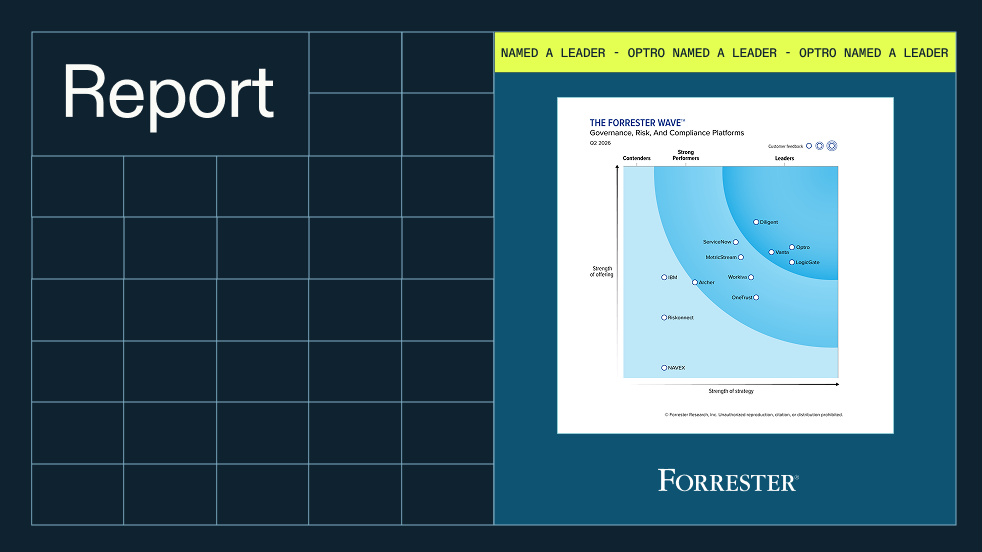
CRX | GRC Intelligence and Agentic AI across audit, risk, and compliance | Read more
October 14, 2026 • 10 min read
Compliance teams are responsible for scoping, running, and proving compliance across a growing portfolio of security frameworks, often with lean teams relative to the scope of the program. Despite GRC platforms, day-to-day work remains largely manual and reactive. In a July 2026 survey of 201 security and compliance practitioners, nearly 90% of respondents said they manually remap or re-document at least some evidence across compliance frameworks.
Compliance shouldn't reset every year to recertify SOC 2, ISO 27001, and other frameworks.
Agentic compliance replaces the fire drill with a program that compounds: every framework you add gets easier because of the ones you've already done.
When the patterns below are in play, each audit cycle starts from something close to zero. Especially where teams run two to five or more active frameworks simultaneously, this model doesn't scale with the business and increasingly puts certification timelines and organizational risk posture in jeopardy.
Scoping a new compliance framework can involve interpreting hundreds of requirements against an organization's existing controls. Optro's 2026 Risk Intelligence Report found that the median enterprise maps its controls to approximately seven frameworks, covering 2,700 requirements. Despite that complexity, organizations rarely document the rationale, so they have to start from scratch every time.
When an organization has prior compliance work to draw on, identifying where it overlaps with a new framework can take days of digging through files. Published crosswalk guides exist, but are generic and don't account for how a specific organization has implemented its controls. The same July 2026 security and compliance report found that 25.9% re-document the same evidence for each framework, and only 6.5% say tooling or templates handle most cross-framework mapping.
Evidence is gathered in bursts around audit time rather than maintained year-round. Stakeholders across engineering, IT, human resources, and legal are chased on accelerated timelines. Even when evidence is collected more frequently, the process is not particularly automated. The 2026 survey found that 42.3% of security and compliance practitioners collect evidence continuously but still rely heavily on manual consolidation.
Whether a piece of evidence actually proves a control or requirement is effective depends on judgment calls and criteria that vary by manager, control, and company. Criteria are rarely written down. Newer team members and auditors ask questions that experienced compliance managers answer from memory — creating both a training gap and an audit risk. Optro research found that nearly 70% of risk professionals lacked consistent reporting on risk and controls data across functions. About 60% had limited or no visibility into issues identified by other teams.
When the auditor’s Prepared/Provided by Client (PBC) list arrives, the four to eight weeks that follow become a mad dash to locate, validate, and package evidence — often revealing gaps the program should have caught months earlier. In the July 2026 security survey, more than half of security and compliance practitioners cited getting time and input from technical teams as an audit-preparation bottleneck, while 36.3% identified coordination across teams as a challenge.
Agentic compliance shifts the work itself. Instead of your team manually scoping requirements, drafting controls, chasing evidence, and testing effectiveness, agents do that work continuously, so your team reviews what matters instead of assembling it from scratch. Every framework you add builds on the understanding already captured for the ones before it, so the program gets easier over time instead of resetting every cycle.
The goal is to keep more of the work audit-ready throughout the year. And because Agentic Compliance integrates with Optro’s connected GRC platform rather than operating as a standalone compliance solution, that work can also support the organization's broader risk program.
Agentic Compliance works to run each stage of the compliance lifecycle, while your team reviews what matters most:
Compliance Agent instantly shows where frameworks overlap, drawing on requirements and information about an organization's compliance environment to suggest applicable controls, evidence, and mappings to other frameworks. For instance, if an enterprise has already assigned owners and documented controls for SOC 2, that information can help inform its ISO 27001 scoping work. The agent can recommend how requirements might apply. Humans, however, remain responsible for deciding what's in scope and whether the controls are appropriate.
Agents draft controls based on the frameworks in scope, generate the test procedures and evidence needed to validate them, and evaluate control effectiveness on an ongoing basis. Instead of a team manually building, documenting, and testing each control, agents handle that work continuously and flag exceptions or gaps for the team to review and resolve.
An ongoing evidence library is maintained through connected systems and automated stakeholder requests. Instead of reconstructing what happened months later during an audit, teams collect and review evidence closer to the activity itself.
Teams can work from live data rather than outdated snapshots. Reporting stays accurate and relevant. When an auditor’s request arrives, the team works from evidence and test results they already have, rather than racing to assemble them under a deadline.
Compliance isn’t a single project; it’s a portfolio problem. The goal of agentic compliance is to simplify that portfolio over time, but the right place to start is with the frameworks most critical to your business today.
SOC 2 and ISO 27001 are common starting points as requirements for organizations that need to demonstrate their information security practices. A SOC 2 examination produces an auditor's attestation report. ISO 27001 certification evaluates whether an organization's ISMS meets the standard's requirements. They aren't interchangeable, but organizations pursuing both don't start with two completely separate security programs. The same access controls, employee training, and other security practices may support requirements in both frameworks.
Agentic compliance helps teams work with that overlap; identify relevant existing controls and evidence, and account for differences between the frameworks. For organizations that already have one framework in place, this can reduce the manual analysis required to add the other. Once those foundational frameworks are in place, the product helps you understand where to go next and simplifies that progression by having agents handle the heavy lifting of scoping, mapping, and evidence reuse along the way.
Compliance shouldn’t have to start over with every new framework, audit cycle, or control review. Agentic Compliance keeps agents working continuously, so your team spends its time on the decisions and judgment calls that need human input, not the manual work. Each framework you add makes the next one easier, not harder. By the time the next audit arrives, it should feel less like a fire drill and more like a formality.