InfoSec
CRX | GRC Intelligence and Agentic AI across audit, risk, and compliance | Read more
June 30, 2026 • 22 min read
Tony Luciani
GRC platforms often look similar in a simple feature list comparison. The real buying challenge is figuring out which tools match your program's complexity and which will require workarounds as you move beyond a single framework or a small team.
This guide is for audit, risk, and compliance leaders evaluating GRC platforms. It compares eight leading GRC tools, explains how to evaluate them, and includes an at-a-glance comparison table to help you make a confident, well-informed choice.
Here are the eight GRC solutions we'll explore:
1. Optro
2. Workiva
3. Diligent One Platform (HighBond)
4. Vanta
5. LogicGate
6. MetricStream
7. Riskonnect
8. ServiceNow GRC
Each GRC platform takes a different approach to scalability, usability, and execution.
This table highlights where the top tools differ most, so you can quickly narrow options based on how your team operates.
Platform | Scales across frameworks | Usability & configurability (without IT) | Time to value (implementation) | ICP/operating model |
|---|---|---|---|---|
Optro | Unlimited frameworks with shared controls and evidence | High — built for practitioners, not technical admins | Fast | Mid-market to enterprise |
Workiva | Strong framework mapping for reporting and disclosure | Medium — powerful but training-heavy | Moderate to slow | Enterprises, public companies |
Diligent One Platform (HighBond) | Broad framework coverage with analytics-driven testing | Medium — steeper learning curve | Moderate | Enterprises, highly regulated orgs |
Vanta | SOC 2, ISO 27001, limited expansion beyond core frameworks | High — very intuitive and guided | Fast | Startups and small teams |
LogicGate | Flexible framework mapping via configurable workflows | Medium — depends on configuration choices | Moderate | Mid-market to enterprise |
MetricStream | Enterprise GRC program modules, typically deployed as a centralized GRC hub with formal governance processes | Medium — admin-led; day-to-day usability depends on program design and training | Moderate to slow | Large enterprises with mature, centralized GRC programs |
Riskonnect | Risk-management-led platform, strong in operational risk/event tracking | Medium — workflow/config dependent | Moderate | Enterprises with dedicated risk operations teams managing incidents, claims, and loss-event reporting |
ServiceNow GRC | GRC workflows designed to run inside the ServiceNow ecosystem | Medium — works well for established ServiceNow users | Moderate to slow | Mid-market to enterprise organizations standardized on ServiceNow |
Note: Support varies by package, so confirm the onboarding model and post–go-live support during your evaluation. Data current as of February 2026.
Different GRC tools can look comparable on paper, but they're optimized for different operating models — reporting and disclosure workflows, audit readiness and control execution, operational risk/event management, or GRC embedded inside an existing enterprise platform.
Each of the following eight tools includes a concise overview, key capabilities, and the use cases for which it's typically chosen.
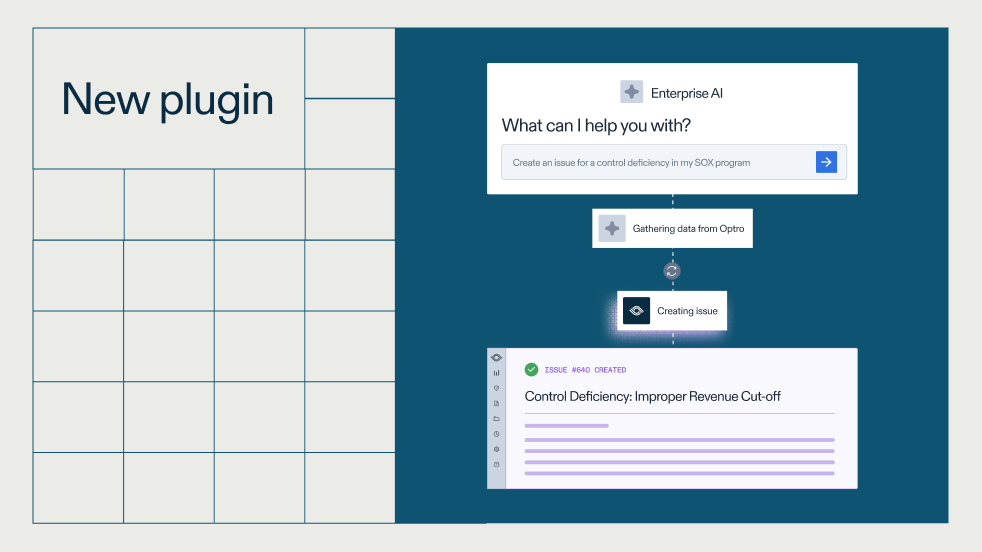
Optro (formerly AuditBoard) is a GRC Intelligence Platform designed to run audit, risk, and compliance as a single, connected program rather than a collection of separate tools. It combines a system of record, the trusted, continuously maintained foundation for your controls, risks, and evidence, with an AI-driven system of action, where AI agents work alongside your team to surface risk, support control testing, and flag issues for review, giving you one platform to manage audit work, track compliance activity, and understand how risk shows up across the organization.
That shared foundation cuts down rework and prevents compliance and risk management programs from drifting as requirements evolve. It also makes growth easier to manage, as you don't need to redesign processes each time the scope expands.
For organizations under regular regulatory scrutiny, Optro pairs a system of record with a system of action to support both daily execution and ongoing oversight. Public companies using Optro's agents for control testing have saved about 70% of their time in year one, part of a broader goal to reduce fieldwork hours by up to 87%. Optro is a strong fit for practitioners who want an easy-to-use, customizable platform that pairs reliable records with AI agents that work alongside the team, while humans review and govern every recommendation.
Features
CrossComply sits at the core of Optro's compliance architecture, using a shared control and evidence layer across audit, risk, and compliance programs. That structure lets teams apply the same work across frameworks — so when you add new standards, you don't have to start over or duplicate effort. Progress continues as the scope expands, making regulatory change far easier to manage.
Best for
Optro is well suited for managing multiple frameworks and aligning cross-functional audit, risk, and compliance across risk registers, control activities, compliance procedures, and compliance reports.
What they say
"What I like best about Optro is how intuitive and user-friendly the platform is. It brings our SOX and operational audits together in one place, which makes collaboration across teams seamless. The automation features save a lot of time by reducing manual work, and the real-time dashboards give great visibility into audit progress and status. Overall, it helps streamline the entire audit process and improves efficiency." —Sara, enterprise internal audit manager
A GRC Intelligence Platform combines two layers: a system of record, which centralizes controls, risks, evidence, and policies in one place, and a system of action, where AI agents work alongside GRC teams on top of that data to help flag emerging risks and support control testing. Humans review, govern, and tune the actions agents recommend, and each step is logged for audit purposes. Optro is built this way; other platforms in this comparison may structure their systems differently.
Workiva is known for enterprise reporting and disclosure workflows.. It's popular among teams that want to connect narrative and numeric reporting, maintain traceability, and support corporate governance requirements involving finance, legal, and compliance stakeholders.
Features
Use case
Workiva prioritizes controlled reporting and disclosure — financial reporting, SEC-style governance workflows, and audit-ready documentation across finance, legal, and compliance.
Diligent One Platform (formerly HighBond) supports governance activities alongside audit, risk, and compliance management. It offers analytics-driven monitoring, workflow automation, and ACL tooling to support continuous monitoring for audit and compliance processes.
Features
Use case
Diligent One Platform (HighBond) is tailored for programs with dedicated analytics capability and regulated environments where monitoring depth and structured oversight are priority requirements.
Vanta is a lightweight trust management platform that focuses on fast audit readiness for SOC 2 and ISO 27001. It relies on integrations and automated testing to support cybersecurity compliance requirements, evidence collection, and ongoing visibility, which may suit smaller teams.
Features
Use case
Vanta works well when the scope is a small set of security frameworks and the priority is maintaining audit readiness with limited internal compliance capacity.
LogicGate Risk Cloud is intended for teams that want to design processes that align with their business practices, connect risk and compliance data, and reduce silos. LogicGate also offers native integrations for systems such as Jira and Microsoft 365 to support a more secure connection between tools and teams.
Features
Use case
LogicGate may be able to help organizations establish clear internal standards for risk and compliance, and define, govern, and maintain consistent workflows across teams.
MetricStream is an enterprise platform for running centralized risk and compliance programs across large organizations. It supports structured workflows for areas like policy and control management, compliance activities, risk management, audit management, and issue remediation, with reporting designed for governance and oversight stakeholders.
Features
Use case
MetricStream is best for large enterprises with formal governance processes and multiple stakeholder groups. It aligns with operating models where workflows are standardized across business units, and reporting is oriented around centralized oversight and program administration.
Riskonnect is a risk management platform commonly used for operational risk programs where event, incident, or loss workflows are central to how risk is tracked and reported. It supports configurable risk registers, assessments, and reporting, and is often evaluated in contexts where risk operations want consistent visibility into risk events and exposures.
Features
Use case
Riskonnect is most commonly considered when event-driven risk visibility is the core buying driver.
ServiceNow GRC is a suite of risk and compliance applications built on the broader ServiceNow platform. It's most often evaluated when teams want work to follow the same operational patterns they already use in ServiceNow — intake, tasking, approvals, and workflow routing — rather than adopting a separate system.
Features
Use case
ServiceNow GRC aligns to environments where the ServiceNow platform is a primary system for work intake, task routing, and operational process management.
Choosing the right GRC tool is a fit question: Can it support how your program actually runs today and keep working as your frameworks, stakeholders, and audit demands expand?
At a high level, the decision usually comes down to four things:
So rather than getting stuck in feature checklists, it helps to run each option through a few practical "fit" checks. The best practices below are a simple way to narrow the field and spot how well a tool aligns with your planned growth.
The fastest way to simplify your selection process is to focus on platforms designed around GRC workflows — controls, evidence, issues, and reporting — rather than tools you'd have to retrofit into a GRC system of record. Flexibility matters, but so does having the right core data model and governance workflow support once scrutiny increases.
A strong GRC tool should adapt to your processes without turning every change into a technical project. If updates require scripting or constant IT support, ownership drifts away from the teams running the program. No-code configuration helps practitioners maintain control.
GRC programs rarely stay static. Make sure the platform can support SOX, ISO, NIST, GDPR, HIPAA, and whatever comes next in a single environment. In practice, scalability is less about how many frameworks a vendor lists and more about whether you can reuse controls and evidence as scope grows.
Capabilities only matter if your team can adopt them quickly and maintain them over time. To assess that, look at typical GRC implementation timelines for programs like yours, how onboarding is structured, and what ongoing support looks like once you're live — especially as requirements change.
These questions help confirm whether a GRC platform can support governance, risk, and compliance strategy over time.
An enterprise-grade GRC tool should support execution and oversight, and not just documentation. It should help your team maintain clear ownership, collaborate across stakeholders, and keep programs aligned as requirements change.
As you compare solutions, look for a platform that connects audit, risk, and compliance work in a consistent system, reduces manual effort through automation, and provides reliable reporting as scope expands.
For mid-market and enterprise organizations that want to run GRC as one connected program instead of separate tools, request an Optro demo to see how a system of record and a system of action work together across audit, risk, and compliance.
In a GRC Intelligence Platform, AI agents work alongside GRC teams to handle tasks like evidence collection, control testing, and continuous monitoring, while humans review, govern, and tune what the agents recommend. Optro, for example, logs every agent action so decisions stay traceable and audit-ready rather than operating as a black box.
Independent research offers one benchmark: an IDC Business Value Assessment of Optro, published in June 2024, found participating organizations saw a 34% reduction in time to make risk-related decisions, 45% more productive audit and compliance teams, and a 50% improvement in stakeholder engagement. Ask any vendor for its own documented, third-party validated results before comparing platforms.
GRC is a broader discipline that spans governance, risk, compliance, audit, ethics, and culture, while integrated risk management (IRM), as defined by Gartner, refers more specifically to technology that unifies strategic, operational, and IT risk management. Many GRC platforms, including those in this comparison, support IRM use cases, so the terms often overlap in vendor materials.
GRC software can help document cybersecurity risk management processes, track incident timelines, and generate reports that support SEC filings such as Form 8-K and Form 10-K, which have required cybersecurity risk disclosures since rules the SEC adopted in 2023. Final materiality determinations and the filings themselves remain the responsibility of company management and legal counsel.
Tony Luciani is a Strategic Account Executive, EMEA at Optro. Prior to Optro, Tony served as IT Risk and Compliance Lead at Sony Pictures. As a former InfoSec consultant, PCI QSA, and HITRUST Assessor, his experience ranges from performing gap/attestation assessments (i.e. NIST, ISO, CIS, SOC2, PCI, HITRUST, etc.) to facilitating IT risk management programs for customers across multiple industries. Connect with Tony on LinkedIn.